WHY IT MATTERS

What "3D Tour Compliance" Actually Means.

A public 3D tour creates four separate risk vectors from the moment it goes live. Most providers are unaware of them. We have built our entire process to address all four of them.

1. Consent

Every tour load is a GDPR-relevant data transfer. No consent gate means you're in violation from first pageview. Is yours documented, contractually covered, and technically implemented? Ours are.


2. Ownership

Once your scan is uploaded, who controls it? Matterport's terms grant them a broad licence over your 3D data. Most providers have never read them. We have - and we've structured every contract to protect your position.

3. Exposure

Every public tour loads images and geometry into the visitor's browser. Every visitor - including AI agents and scrapers. Self-hosted 3D tours and Gaussian Splats put the complete model in the browser - fully unprotected. This is the risk nobody talks about. We have a solution.

4. Security

Alarm panels. Emergency routes. Security zones. Floor plan geometry precise enough to plan something you don't want planned. What's your protocol for what goes live - and what doesn't? We have one. For every project.

"The cloud is half the question. The browser is the other half."

Everyone talks about where the data is stored. Nobody talks about what happens when a tour loads in a visitor's browser. We do.

Standard workflow vs. Compliance path

Click through both. The same job, done two different ways. Click any step in the standard workflow to see what's at stake. Then click the matching step below to see how we handle it.

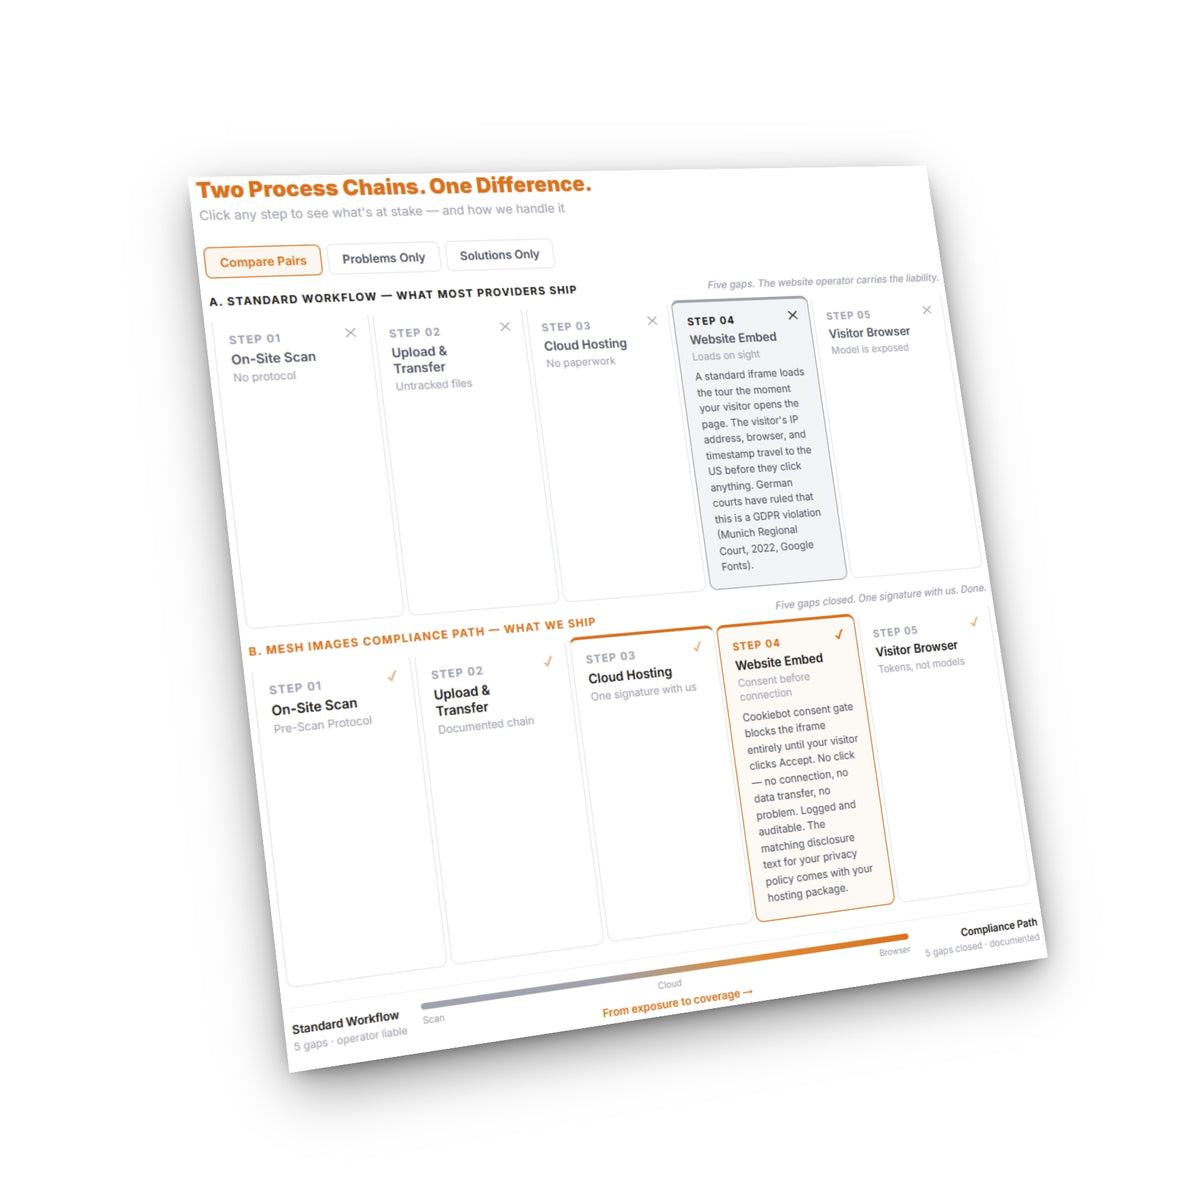
Two Process Chains. One Difference.
Click any step to see what's at stake — and how we handle it

A. Standard Workflow — what most providers ship

Five gaps. The website operator carries the liability.

✕

Step 01

On-Site Scan

No protocol

No documented rules for what gets captured. Alarm panels, server room doors, names on letterboxes can end up in a public tour. Persons walking through the scan are not always blurred. The scan operator may keep copies you don't know about.

✕

Step 02

Upload & Transfer

Untracked files

Scan files travel from the camera through unknown systems to the cloud. No agreement covers this leg. If a tablet or laptop gets lost in transit, nobody can prove what was on it — or that it was deleted afterwards.

✕

Step 03

Cloud Hosting

No paperwork

Tour stored on US servers. No data processing agreement signed with you. If your DPO asks for documentation, nobody can produce it. If something goes wrong, no contractual chain shows who handles what.

✕

Step 04

Website Embed

Loads on sight

A standard iframe loads the tour the moment your visitor opens the page. The visitor's IP address, browser, and timestamp travel to the US before they click anything. German courts have ruled that this is a GDPR violation (Munich Regional Court, 2022, Google Fonts).

✕

Step 05

Visitor Browser

Model is exposed

This is where most providers fail — and where most clients never look. Self-hosted virtual tours and Gaussian Splat alternatives load the entire 3D model into the visitor's browser. Open for any AI agent to scrape.

B. MESH IMAGES Compliance Path — what we ship

Five gaps closed. One signature with us. Done.

✓

Step 01

On-Site Scan

Pre-Scan Protocol

Documented protocol on every project. GPS off. Security elements covered or excluded. Persons blurred or rescanned. Scan partner under written contract — files deleted after upload, deletion confirmed in writing.

✓

Step 02

Upload & Transfer

Documented chain

Scan files travel through documented infrastructure only. Encrypted transfer. Scan partner deletion logged and dated. Your AVV with us covers this step end-to-end.

✓

Step 03

Cloud Hosting

One signature with us

One AVV with us. The Matterport contract chain is already signed by us — including EU Standard Contractual Clauses. Your DPO gets one paper, not five.

✓

Step 04

Website Embed

Consent before connection

Cookiebot consent gate blocks the iframe entirely until your visitor clicks Accept. No click — no connection, no data transfer, no problem. Logged and auditable.

✓

Step 05

Visitor Browser

Tokens, not models

Matterport delivers tour content as time-limited signed tokens via CDN. Cubemap tiles instead of source mesh — the full 3D geometry never reaches the browser.

Standard Workflow

5 gaps · operator liable

Scan Cloud Browser
From exposure to coverage →

Compliance Path

5 gaps closed · documented
How We Do it

OUR PROCESS

Compliance by Design

Most providers treat compliance as annoying paperwork - something you add at the end. We built it into every step. Unobtrusive. From the moment we plan a scan to the day a tour goes live on your website, five checkpoints run in sequence. Every project. No exceptions.

Download Compliance Brief

PRE-SCAN PROTOCOL

Before We Scan - We Decide What Stays Out.

Security-sensitive areas are physically covered or excluded before the first scan point is set. What gets captured, what stays out, and what happens to the files afterwards is documented in writing. For every project.

Download Compliance Brief

DPA

Contracts Before Scan - Always.

Before we start, the paperwork is done. You sign one Data Processing Agreement (DPA) with MESH IMAGES. The Matterport contract chain - including EU Standard Contractual Clauses - is already signed by us. Your Data Processing Officer (DPO) gets one document, not five.

Download Compliance Brief

CONSENT GATE

The Tour Doesn't Load Until the Visitor Says Yes.

A standard embed connects to US servers the moment your page loads - before the visitor clicks anything. That's a GDPR violation from pageview one. We block the connection entirely until the visitor actively consents. No consent, no connection, no data transfer.

Download Compliance Brief

TOUR VERSIONS

One Tour for the Public. One for the People Who Work With It.

If necessary, we produce two versions. The public marketing tour is deliberately scoped - no sensitive areas, no security details. Whereas the B2B tour carries full details, is password-protected, and is used for technical planning and operations - with controlled user access.

Download Compliance Brief

COMPLIANT HOSTING

Compliant on Day One. And Every Day After.

Compliance doesn't end when the tour goes live. Hosting with MESH IMAGES means: We monitor platform changes and flag anything that affects your data position before it becomes a problem. Deletion is documented. And if something shifts, you hear from us first.

Download Compliance Brief

One AVV. One signature. Done.

Every MESH IMAGES project ships with a fully pre-filled Data Processing Agreement under GDPR Art. 28. You review, you sign. We handle everything else.

THE HONEST COMPARISON

Self-Hosted Doesn't Mean Compliant.

There is no perfect solution. But there is a best one.

Self-Hosted (3DVista, Pano2VR)

Hosting on a German server solves one thing: the cloud-side data transfer to the US. That's real. But it doesn't solve the browser problem. A self-hosted tour still loads assets directly into the visitor's browser - with no dedicated security team behind it, no active countermeasures against extraction tools, and no institutional architecture protecting your location's geometry. You own the server. You own the risk.

3D Gaussian Splats (XGrids)

Visually striking. Technologically interesting. And structurally the weakest option for public compliance. The .splat file is transferred completely to the client browser - every visitor gets the full model. There is no access control at geometry level. For internal use cases, this can make sense. For a public marketing tour of a large location, it doesn't.

Matterport via MESH IMAGES

Matterport is the only platform in this market with an institutional security function actively working against extraction tools - changing API endpoints, token structures, and URL-signing logic as known extraction workflows emerge. Combined with our consent gate, signed DPA, pre-scan protocol, and two-version architecture, it is the only end-to-end compliant option for public marketing tours of large locations.

WHAT WE WON'T HIDE

We Recommend Matterport. Here's the Full Picture.

We've worked with Matterport since 2015. We know the platform better than most. And we think the best thing we can do for you is be straight about how it works - the strengths and the open questions.

Your data stays yours.

The EU Data Act (Sept. 2025) gives you enforceable rights to portability and deletion. Full export - including Matterpak, Panoramas and E57 point cloud - is available at manageable cost. Deletion on request is initiated by us, in writing, with confirmation. We clarify both before the project starts.

US platform. EU contracts. CoStar. All handled.

Matterport hosts data in the United States. We've signed the EU Standard Contractual Clauses - every project inherits that coverage automatically. CoStar acquired Matterport in February 2025. Nothing has changed in the compliance documentation. We monitor it and tell you if anything does.

One limitation we always name.

Matterport retains a licence over anonymised, aggregated spatial data derived from scans. It doesn't affect your data rights. But we name it in every contract - and negotiate an additional clause where needed. No-AI clause available as standard.

Matterport is not a lock-in silo. Your data stays yours.

Your scan data is exportable. Your contract is clear. And if Matterport ever becomes the wrong answer, we'll tell you - and we'll have a migration path ready.

CLEAR LINES

What We Handle. What Stays With You.

The following table does not constitute legal advice. All AVV and compliance documents must be reviewed by a qualified data protection attorney or certified DPO before operational use.

MESH IMAGES handles

  • Consent gate implementation
  • AVV with you under GDPR Art. 28
  • Matterport DPA with SCCs signed
  • Pre-scan protocol
  • Technical and organisational measures (TOMs)
  • Optional two-version tour architecture (public + B2B)
  • Deletion on request, documented

And the Monitoring of platform changes (Matterport, CoStar)


You remain responsible for

  • Your own privacy policy (updated to reference Matterport as subprocessor)
  • Final sign-off by your DPO or legal advisor
  • Publishing the compliant embed on your website
  • Any sector-specific obligations (KRITIS, NIS2, DORA)
  • Responding to visitor complaints or DPO enquiries
  • Internal staff training on data handling
  • Your own records of processing activities (Art. 30)


STRAIGHT ANSWERS

FAQs

The Questions We Actually Get Asked.

Is Matterport GDPR-compliant?

It depends on how it's set up. Matterport as a platform gives you the right contracts to work with. But those contracts don't activate themselves - someone has to sign them, implement the consent gate, and document everything. With MESH IMAGES, that's all done before your tour goes live.

What happens if a tour is embedded without a consent gate?

The moment your page loads, your visitor's browser connects to Matterport's servers in the US - sending their IP address and session data before they've clicked anything or agreed to anything. Under GDPR, that's illegal. German courts have already ruled on exactly this kind of situation (Google Fonts, Youtube, Google Maps, etc.). You're exposed from the very first visitor.

Matterport stores data in the US. Is that a problem?

Not if the paperwork is right. Any time personal data travels from the EU to the US, EU law requires a legal contract to be in place - one that ensures your data is treated the same way it would be in Europe. Matterport has signed that contract. We've verified it, signed it on our end, and include it in every client project. Your data goes to the US - but it goes there legally, with documented protections.

We have existing tours without consent gates. What now?

If you're already a hosting client with MESH IMAGES, you can add our compliance package directly. If your tours are currently hosted elsewhere, get in touch - we'll assess whether a transfer to MESH IMAGES makes sense for your setup and give you a proposal.

What happens to our data if we end the contract?

You can request full deletion - Matterport is contractually required to delete your data within 30 days. This doesn't happen automatically, and managing the deletion process, getting written confirmation, and documenting it in your project file is part of our GDPR Compliant Hosting service.

Is compliance included in the price?

Compliance is available as part of specific hosting packages. But here's the important part: it's you - the location operator - who publishes the tour on your website. That makes you responsible for how it's embedded, consented to, and documented. We provide everything you need to get that right. Whether you use it is your decision.

How well is our location's data actually protected once the tour is live?

It depends entirely on which platform you're using.

With Matterport, the actual 3D geometry never reaches the visitor's browser. What gets delivered are small, time-limited tiles that expire after use. On top of that, Matterport has a dedicated security team that actively monitors for extraction attempts and closes known loopholes. No system is 100% sealed - but Matterport is the hardest target available.

With self-hosted tours, the assets load directly into the visitor's browser with no institutional security behind them. It solves the cloud-side data transfer question - but makes the browser exposure problem worse, not better.

With Gaussian Splatting, the complete 3D file is transferred to the visitor's browser in full. Every visitor gets the whole model. For internal use cases that can be fine. For a public marketing tour of a large location, it's the weakest option

Selfhosted solutions solve one problem (hosting) and create another (extraction).